[FIN]CROSS-BORDERVOL: $4.2T
[SEC]CYBER ALERT: TIER2
[POL]IS0 GROWTH:+14%
[GEO] CLOUDINDEX: +2.4%
Structural Logic
Category Filters
How often should smart terminals receive security updates?
Lead Author
Published
Views:
How often should smart terminals receive security updates?
Smart terminals should undergo a security patch review at least monthly, with updates deployed sooner when a vulnerability creates an immediate risk. For payment terminals, self-service kiosks, and connected classroom devices, the right cadence depends on exposure, vendor support, and the consequences of compromise—not one universal schedule.
A practical policy combines a predictable maintenance window with an emergency update process. Routine patches can follow a tested monthly rollout. A remotely exploitable flaw affecting an exposed terminal may require action before that window, particularly if attackers are already exploiting it. If a safe patch is unavailable, containment should not wait.
The important distinction is between reviewing updates and installing them. A monthly review is a useful baseline; it is not permission to leave urgent vulnerabilities untreated for a month.
What is a sensible update schedule for a terminal fleet?
Set separate expectations for vulnerability monitoring, risk assessment, and deployment. Otherwise, a policy saying “monthly updates” can hide several weeks between a vendor advisory and anyone deciding whether it matters.
The following is an operational starting point, not a universal compliance timetable. Deployment deadlines should be tightened where contracts, applicable standards, or actual exposure demand it.
A terminal fleet also needs periodic reconciliation: which devices actually received the update? Offline kiosks, spare payment readers, and classroom displays used only occasionally can miss several deployment cycles without attracting attention.
Which vulnerabilities should interrupt the normal maintenance window?
A severity score helps, but it does not settle the decision. Ask whether the affected component exists on your terminals, whether the vulnerable feature is enabled, and whether an attacker can reach it. Then consider what successful exploitation would allow: extracting credentials, changing payment behavior, accessing personal data, or controlling the device remotely.
For example, a public kiosk running a vulnerable browser engine may need rapid attention even when its operating system is current. A classroom display with an exposed remote-management service deserves a different response from the same model on a tightly restricted network. Neither situation can be judged from the device name alone.
The Cybersecurity and Infrastructure Security Agency’s Known Exploited Vulnerabilities catalog is one useful signal for prioritization. Its inclusion of a vulnerability indicates evidence of exploitation, but organizations still need to establish whether their installed versions are affected. Catalog deadlines are not automatically binding on every private-sector operator.
When exploitation is credible and exposure is real, act while testing proceeds. Depending on the system, that may mean disabling remote access, restricting network paths, removing a vulnerable function, or temporarily withdrawing the terminal from service. Network segmentation reduces exposure; it does not repair vulnerable software.
Does updating the operating system cover the whole terminal?
Usually not. “Smart terminal” describes a service endpoint, not a single software layer. A self-service kiosk may contain an operating system, browser runtime, kiosk application, device-management agent, printer controller, and separate payment component. Each can have its own update source and support lifecycle.
Payment environments make this especially important. The retailer may manage the POS application while an acquirer or terminal provider controls payment-device firmware. An application release cannot be assumed to include operating-system fixes, and a firmware update does not necessarily address a vulnerable cloud integration.
Maintain an inventory that records the model, installed versions, responsible supplier, support end date, and deployment method. Where available, component inventories or software bills of materials can help identify affected dependencies. They still need to match what is actually deployed.
This layered view fits the cross-sector perspective of Global Modern-Service & Smart-Terminal (G-MST): terminal hardware, SaaS management platforms, payment infrastructure, and education technology must be assessed together. A current device can still depend on an unsupported management service—or the reverse.
How can updates be tested without leaving terminals exposed?
Use a short, risk-based test cycle rather than treating every patch as a full product launch. Testing should reproduce the functions that would make a failed update operationally expensive.
For a retail checkout, that means more than confirming that the screen turns on. Check transaction processing in an approved test environment, peripheral connectivity, receipt printing, network recovery, and management-console reporting. For a classroom terminal, check sign-in, touch input, teaching applications, and access restrictions. A public kiosk may need accessibility and unattended-recovery checks.
A representative pilot group should include relevant differences: hardware revisions, peripheral combinations, connectivity conditions, and application versions. Testing only the newest device on a fast office network can miss the failure that affects an older kiosk using a cellular connection.
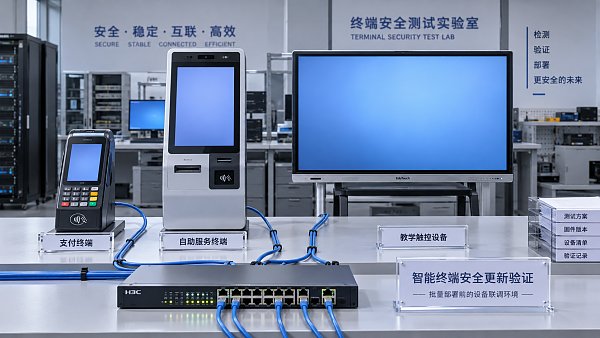
Deploy in stages, inspect the results, and expand once the agreed checks pass. For urgent patches, shorten the observation period and increase monitoring rather than simply eliminating validation.
Rollback also needs care. Returning to a vulnerable release may restore service while reopening the original exposure. Some firmware cannot be downgraded, and payment devices may require provider-controlled recovery. Establish the supported recovery path before deployment; do not assume a backup alone solves the problem.
Do payment-security and privacy requirements specify an update frequency?
Sometimes, but the scope matters. PCI DSS v4.0.1 Requirement 6.3.3 requires applicable critical or high-security patches and updates, identified through the required risk-ranking process, to be installed within one month of release. Other applicable security patches and updates must be installed within a timeframe determined by the entity.
That requirement applies to systems within the relevant PCI DSS scope; it is not a universal rule for every connected display or kiosk. Nor should one month become the default waiting period for an actively exploited flaw. Operational risk may justify a much faster response.
GDPR does not prescribe a universal monthly patch schedule. Its security obligations are risk-based, including appropriate technical and organizational measures. Likewise, a broad reference to ISO or IEC standards does not establish a device-specific deployment deadline without identifying the applicable standard and requirements.
For payment-device changes, confirm the supplier’s approved update route and any acquirer or payment-scheme conditions. Keep records of applicability decisions, testing, deployment, and exceptions. A release note proves that a patch exists—not that your fleet installed it.
Should terminals update automatically?
Automation is valuable when it provides control and evidence. Unrestricted installation at any hour can interrupt a checkout queue or restart a teaching display during a lesson. Disabling automatic updates indefinitely creates the opposite problem: vulnerable devices that depend on someone remembering to visit them.
The better model is centrally managed deployment with maintenance windows, pilot groups, authenticated update delivery, and status reporting. Devices should verify update authenticity, and administrators should restrict who can approve or distribute packages.
Define what happens when a device misses its window. A terminal returning after weeks offline should be checked for outstanding fixes before resuming sensitive operations. Also distinguish “package delivered” from “installation completed”: some updates require a restart, and a successful download does not prove that the running version changed.
Track failed installations separately from unavailable devices. Repeatedly retrying a patch against insufficient storage or an incompatible firmware branch will not resolve the underlying fault.
What should buyers ask suppliers about security support?
Update frequency is partly a procurement decision. A device intended to remain installed for years is a poor fit if its security support expires much earlier. Ask for written commitments, not just “regular updates.”
- What is the security-support end date for this exact model and software branch?
- Who supplies fixes for the operating system, firmware, bundled applications, and third-party components?
- How are urgent vulnerabilities communicated, and what response commitments apply?
- Can updates be staged, verified remotely, and recovered through a supported procedure?
- Are management tools, security updates, or extended support subject to separate fees?
A promise of frequent releases is less useful than clear ownership and a reliable emergency process. Hardware warranties, product certification, and security-maintenance commitments answer different questions; none should be used as a substitute for the others.
What if a terminal cannot be patched?
Establish why: temporary deployment failure, missing vendor fix, application incompatibility, or end of support. Each needs a different response. Document the affected devices, exposure, interim controls, responsible owner, and deadline for resolution.
Restricted network access and reduced functionality may buy time, but they should not turn an unsupported terminal into a permanent exception. If the device handles sensitive data and cannot be maintained safely, replacement or withdrawal may be the more defensible choice.
Start with three checks: identify terminals that missed their latest applicable update, confirm which models are approaching support expiry, and test the emergency deployment process. Those checks reveal whether a monthly patch policy is working—or merely written down.
Tags
Recommended for You
 How to choose a target country for market penetration in EuropePlan Market Penetration in Europe with confidence. Learn how to compare demand, regulations, competition, and delivery costs to choose the right country for sustainable growth.Oct 15, 2026Lina Cloud
 ISO/IEC 27001:2026 Officially Published for Information Security ManagementISO/IEC 27001:2026: Explore the reported update for cloud CRM, payment gateways and AI-ERP. Discover what to verify before planning certification and procurement changes.Oct 15, 2026Marcus Trust
 How to verify food-grade compliance for wholesale locust bean gumEvaluating locust bean gum wholesale suppliers? Learn how to verify food-grade compliance, check batch reports, and confirm traceability to reduce sourcing risks and buy with confidence.Oct 14, 2026Marcus Trust
 Best Enterprise Tools for Cross-Border Video Privacy: What to CompareCompare the best enterprise tools for cross-border video privacy compliance. Explore data residency, access controls, redaction, and retention to choose the right solution.Oct 15, 2026Marcus Trust
 Which Privacy Platforms Support GDPR, CCPA, and Cross-Jurisdiction Workflows?Which privacy platforms support cross-jurisdiction compliance? Compare GDPR and CCPA workflows, data discovery, and audit evidence to shortlist the right solution.Oct 14, 2026Marcus Trust
 How often should smart terminals receive security updates?How often should smart terminals receive security updates? Discover practical patch schedules, urgent threat priorities, and safe rollout strategies to protect devices and reduce downtime.Oct 15, 2026Lina Cloud
 What happens to school data when a cloud contract ends?What happens to school data when a cloud contract ends? Learn how to secure usable exports, manage access deadlines, and verify deletion to protect student records and avoid costly exit risks.Oct 14, 2026Professor Sarah Ed
 How to clear jams safely in an automatic lentil splitting machineAutomatic lentil splitting machine jammed? Learn safe lockout steps, approved clearing methods, and restart checks to protect operators and reduce repeat blockages.Oct 13, 2026Marcus Trust
 How to keep AI-assisted learning content aligned with course goalsAI assisted learning content: learn how to align lessons, quizzes, and feedback with course goals using clear objectives, expert review, compliance guardrails, and learner data.Oct 12, 2026Professor Sarah Ed
 What documents should a bulk defoamers exporter provide?Bulk defoamers exporter documentation guide: discover essential SDS, CoA, TDS, customs, transport, and compliance files for safer global sourcing.Oct 11, 2026Marcus Trust
 How to evaluate PCI DSS compliance tools for continuous control monitoringPCI DSS compliance tools: learn how to evaluate continuous control monitoring, evidence quality, integrations, and remediation workflows for audit-ready security.Oct 10, 2026Lina Cloud
 When is an FRP fish tank a better choice than glass?FRP fish tank vs. glass: discover when fiberglass offers superior durability, custom shapes, outdoor resilience, and easier installation for your aquarium project.Oct 09, 2026Marcus Trust
 What yield should a commercial salmon filleting machine deliver?Fish filleting machine commercial for salmon: learn how to evaluate realistic yield, saleable output, throughput, trim quality, labor needs, and supplier trial results.Oct 08, 2026Marcus Trust
 How to calculate enclosed belt conveyor capacity for bulk materialsEnclosed belt conveyor capacity explained: calculate bulk-material throughput with effective area, belt speed, density, fill limits, and practical design checks.Oct 07, 2026Lina Cloud
 How to verify an electronics recycling certification before hiring a recyclerElectronics recycling certification verification made simple: check validity, scope, accreditation, data security, and downstream controls before hiring a recycler.Oct 06, 2026Marcus Trust
 How to verify CE compliance for a rotary rack oven before purchaseRotary rack oven CE verification made simple: check model-specific declarations, markings, gas and electrical documentation before purchase to prevent costly compliance delays.Oct 05, 2026Marcus Trust
 How to prevent nutrient runoff from aquaculture waste managementAquaculture & Fishery waste management: prevent nutrient runoff with smarter feeding, solids capture, sludge control, treatment, and monitoring.Oct 04, 2026Marcus Trust
 How to verify safety documentation when buying organic solvents wholesaleOrganic solvents wholesale buyers: learn how to verify SDS, CoA, labels, batch traceability, and transport records before delivery. Reduce compliance risks and purchase with confidence.Oct 03, 2026Marcus Trust
 What hygiene standards should a stainless steel cattle slaughtering line meet?Stainless steel cattle slaughtering line hygiene standards: explore hygienic design, zoning, drainage, sanitation, and compliance essentials for safer beef processing.Oct 02, 2026Marcus Trust
 Digital classroom integration examples that improve lesson flowDigital classroom integration examples that improve lesson flow, connect teaching tools, streamline support, and create reliable, engaging learning experiences.Oct 01, 2026Professor Sarah Ed
 Which CE documents should accompany peanut shelling machines?Peanut shelling machines CE guide: learn which documents—Declaration of Conformity, manuals, technical files, and risk assessments—protect imports and compliance.Sep 30, 2026Marcus Trust
 How to verify whether organic Tribulus terrestris extract is certifiedVerify tribulus terrestris extract organic certification with confidence. Learn how to check certificate scope, botanical identity, certifier validity, lot traceability, and processing details.Sep 29, 2026Marcus Trust
 How to prevent uneven feed in a stainless liquid adding machineStainless liquid adding machine feed issues? Learn practical ways to prevent uneven dosing, reduce air leaks, stabilize flow, and improve production consistency.Sep 28, 2026Lina Cloud
 How to verify aquaculture utilities compliance before a site auditAquaculture utilities compliance: learn how to verify water, power, wastewater, alarms, and records before a site audit to reduce risk and prove control.Sep 27, 2026Marcus Trust
 How to size a tunnel oven for a biscuits factory’s target outputTunnel oven for biscuits factory sizing: learn how to match output targets, band loading, bake time, zones, and cooling capacity for reliable production.Sep 26, 2026Lina Cloud
 What purity specifications matter when sourcing bulk magnesium stearate in North America?Bulk magnesium stearate North America buyers: learn the purity specifications that protect quality, compliance, and production performance.Sep 25, 2026Marcus Trust
 How classroom devices can support healthier screen time habitsScreen time classroom devices can build healthier learning habits when lessons balance focus, movement, collaboration, and purposeful digital tasks. Explore practical strategies today.Sep 24, 2026Professor Sarah Ed
 How often should digital signage content refresh for retail displays?Digital signage content refresh rate for retail displays: discover practical schedules for campaigns, pricing, live updates, and customer engagement.Sep 23, 2026Digital Signage
 How to compare wholesale water pumps for farming by flow rateWholesale water pumps for farming factory guide: compare flow rate, total dynamic head, efficiency, and supplier testing to select reliable irrigation pumps.Sep 22, 2026Lina Cloud
 How North America's service-led economy is changing CRM prioritiesService-led Economy North America is reshaping CRM priorities around customer lifecycle, service data, privacy, payments, and connected experiences. Explore practical strategies for smarter CRM investment.Sep 21, 2026Lina Cloud
 What drives carrageenan gum price differences between suppliers?Carrageenan gum price differences reflect grade, dosage efficiency, quality control, certifications, and supply reliability. Compare true landed cost to choose the best-value supplier.Sep 20, 2026Marcus Trust
 How to choose rugged smart terminals for cold storage operationsRugged smart terminals for cold storage: learn how to evaluate batteries, scanning, wireless coverage, glove usability, and durability for reliable operations.Sep 19, 2026Digital Signage
 What makes smart terminals for healthcare suitable for clinical workflows?Smart terminals for healthcare improve clinical workflows with secure integration, hygienic design, reliable connectivity, and lifecycle control. Explore key evaluation factors.Sep 18, 2026Dr. Hideo Tanaka
 What drives pharmaceutical packaging materials price changes?Pharmaceutical packaging materials price changes explained: assess commodity costs, capacity, compliance, logistics, and supplier risk to negotiate smarter.Sep 17, 2026Marcus Trust
 How to vet ODM suppliers using sourcing intelligenceSourcing Intelligence helps you vet ODM suppliers beyond price—verify capabilities, compliance, quality controls, and supply-chain resilience before launch.Sep 16, 2026Lina Cloud
 What drives seafood packaging machine price differences?Seafood packaging machine price differences reflect automation, hygiene, format flexibility, and service scope. Compare costs wisely to improve uptime and pack quality.Sep 15, 2026Marcus Trust
 How to verify a medical equipment certification service before hiringMedical equipment certification service verification guide: check accreditation scope, market recognition, technical competence, report traceability, and contract terms before hiring.Sep 14, 2026Marcus Trust
 What to check before choosing a drip irrigation systems factoryDrip irrigation systems factory checklist: assess quality control, materials, hydraulic performance, compatibility, compliance, and delivery reliability before buying.Sep 13, 2026Lina Cloud
 How to verify that apple cider vinegar powder is food gradeApple cider vinegar powder food grade verification: review identity, COAs, supplier controls, contaminants, legal compliance, and traceability for confident sourcing.Sep 12, 2026Marcus Trust
 What should you verify before choosing a ledger management supplier?Ledger management supplier checklist: verify posting integrity, audit trails, security, integrations, reconciliation, resilience, and exit readiness before you commit.Sep 11, 2026Lina Cloud